
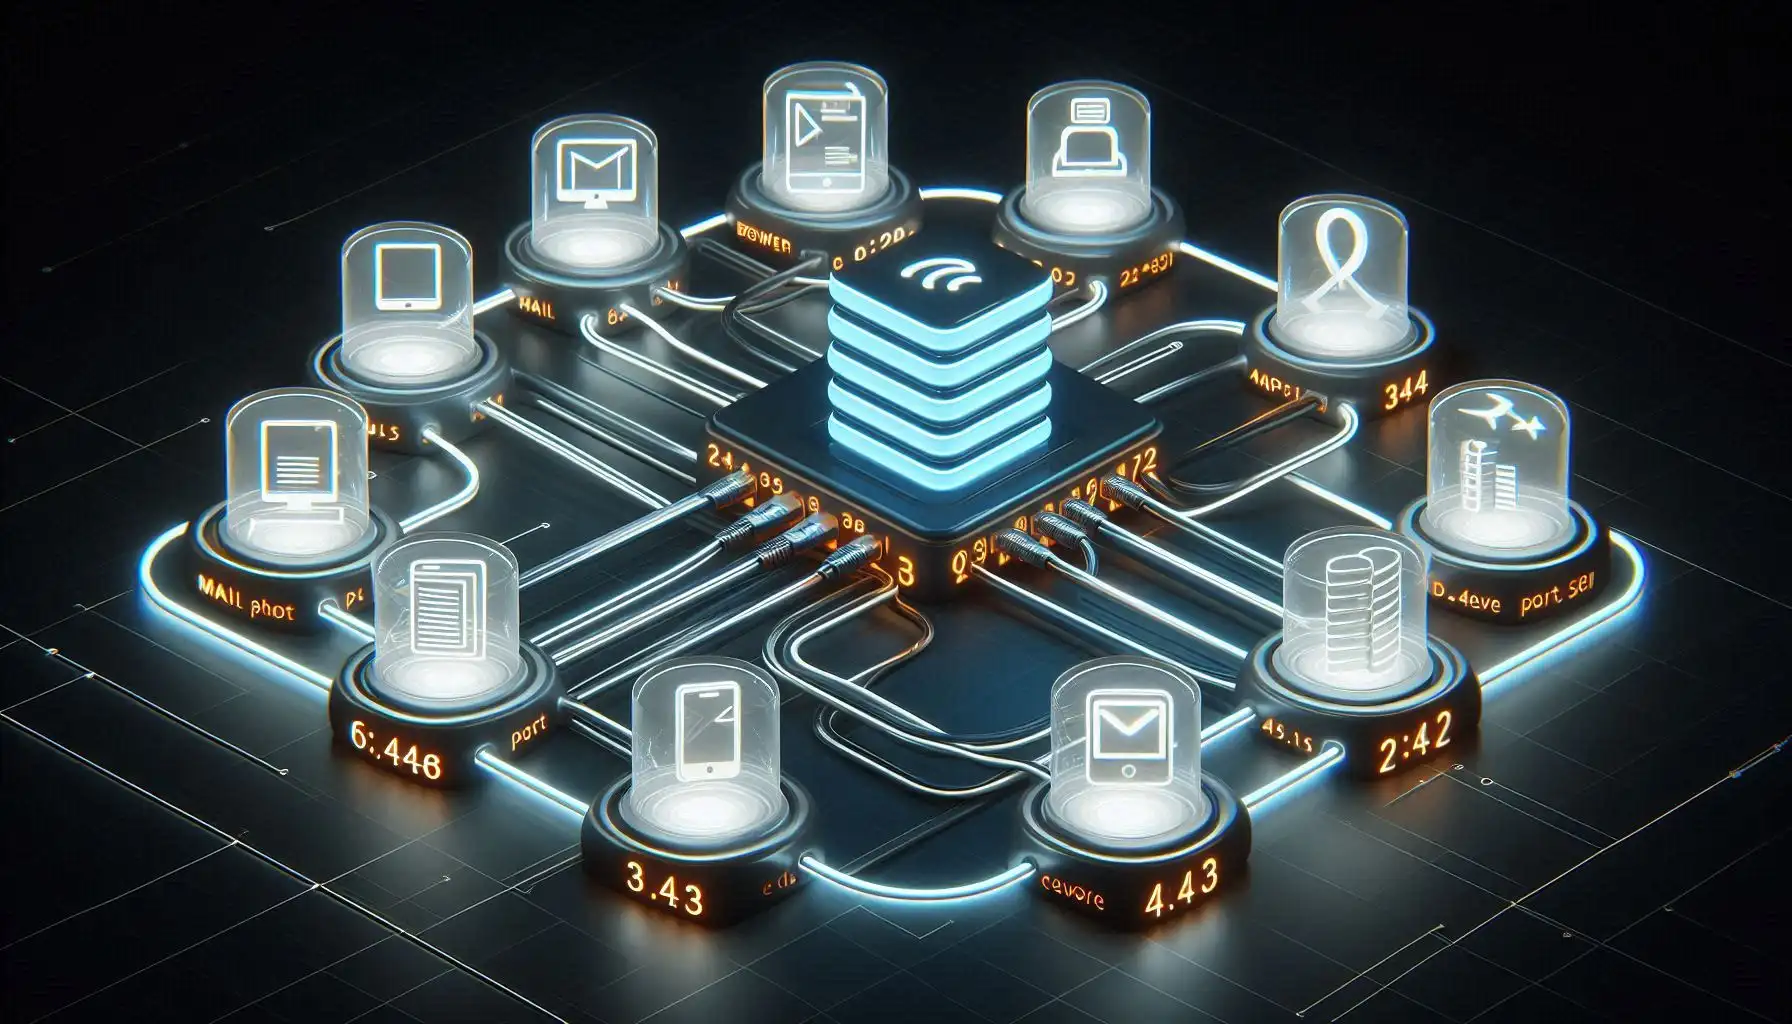
An IP address identifies the destination interface, while a transport protocol and port help identify a communication endpoint. One server can run web, SSH, and mail services on different ports. Always include the protocol: TCP port 53 and UDP port 53 are distinct endpoints.
A port number does not prove a service's identity
TCP and UDP use 16-bit port fields, giving numbers from 0 through 65535. Port 0 is not an ordinary service port. A familiar number suggests a service, but applications can be configured differently. Finding a listener on TCP 443 does not prove that it is a trustworthy HTTPS server.
A client's source port is usually selected temporarily. A browser might connect from its local ephemeral port to a server's port 443. TCP provides reliable, ordered byte delivery within a connection. UDP does not guarantee delivery or ordering, but an application using UDP can implement its own verification and reliability mechanisms.
Common services and their usual ports
| Service | Usual port | Important distinction |
|---|---|---|
| SSH / SFTP | TCP 22 | SFTP is a separate SSH-based protocol, not simply encrypted FTP. |
| HTTP | TCP 80 | Commonly used for unencrypted HTTP. |
| HTTPS | TCP 443; commonly UDP 443 for HTTP/3 | HTTP/3 uses QUIC; a TCP-only test has different coverage. |
| DNS | UDP and TCP 53 | Do not treat DNS as UDP-only. |
| SMTP / submission | TCP 25 / 587 / 465 | Common roles are server relay, submission, and implicit-TLS submission respectively. |
| IMAP / POP3 | TCP 143 / 110; implicit TLS 993 / 995 | STARTTLS on 143 or 110 depends on configuration. |
| FTP | TCP 21 control | Data connections depend on active/passive mode; they are not limited to port 20. |
| MySQL / PostgreSQL | TCP 3306 / 5432 | A database listener does not automatically need public exposure. |
| NTP / SNMP | UDP 123 / 161; traps 162 | Inspect service configuration and source restrictions separately. |
| SMB / RDP | TCP 445 / TCP and UDP 3389 | Remote access requires an appropriate access policy. |
These are reminders, not substitutes for the application's configuration. A broader reference is the IANA port registry. Knowing the port of a management interface or data store does not justify exposing it publicly.
Listening locally does not establish external reachability
On Linux, inspect local listeners, bind addresses, and processes where your permissions allow:
sudo ss -lntupA service bound to 127.0.0.1 listens on IPv4 loopback. 0.0.0.0 indicates an IPv4 wildcard bind, but a firewall or NAT can still prevent external access. Test rather than assume whether an IPv6 listener also accepts IPv4 connections.
On Windows, list local connections and test TCP connectivity to an authorized destination:
netstat -ano
Test-NetConnection example.com -Port 443
TcpTestSucceeded reports a TCP connection test. It does not validate UDP, a TLS certificate, or the application's health. When a connection times out, inspect the bind address, host firewall, cloud rules, and routing as separate stages.
References: ss, Test-NetConnection, and HTTP/3.
Related Articles
Comments ()
Leave a Comment
Sponsors



Apps

