
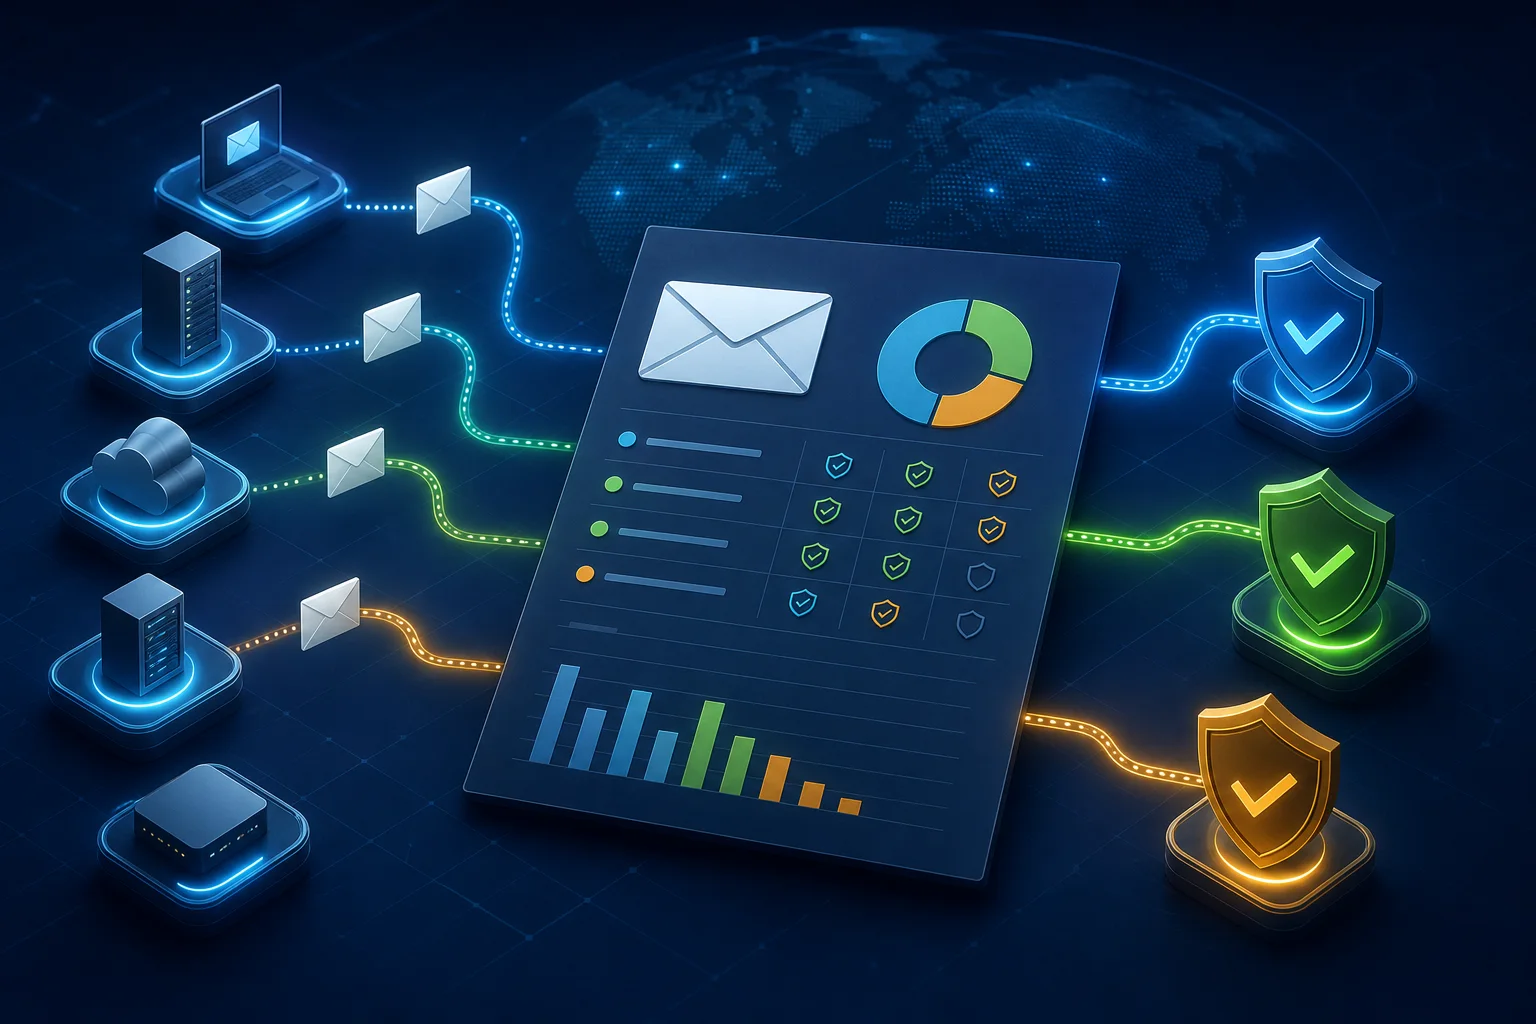
A DMARC aggregate report is a periodic view of mail sources claiming to send for a domain. It can help find legitimate systems that were missed during setup, as well as unexpected senders. The XML is evidence about authentication results, not a complete inventory of every message.
Read the report header first
Check the reporting organization, the domain and the report's start and end timestamps. Reports may arrive late and cover a different interval than your local mail logs. Several providers can send reports with different formats or optional fields.
Group records by source and result
For each record, note the source IP, message count, evaluated disposition, and SPF and DKIM results. DMARC alignment is about whether an authenticated domain aligns with the visible From domain; a raw SPF pass alone does not mean that DMARC passed. Forwarding can alter SPF results while DKIM may survive, depending on message changes.
Map source IPs to known mail services and business owners before changing policy. Ask the provider or application owner to confirm the sending domain and authentication configuration. Do not treat an unfamiliar IP as malicious until you have considered a vendor, relay or forwarding path.
Use the evidence to plan a policy change
Start from the actual message flows and confirm that SPF and DKIM records are correct for each authorized sender. Use aggregate reports to observe the effect over representative business cycles. Move toward a stricter policy only when legitimate sources are understood and the organization's mail owner approves the change.
DMARC XML may contain operational details about mail infrastructure. Limit access to reports and avoid publishing raw files. The original DMARC specification defines the reporting fields and policy mechanism; your provider's parser can make repeated reports easier to compare, but verify its interpretation against the underlying records.
Related Articles
Comments (0)
Leave a Comment
Sponsors



Apps

