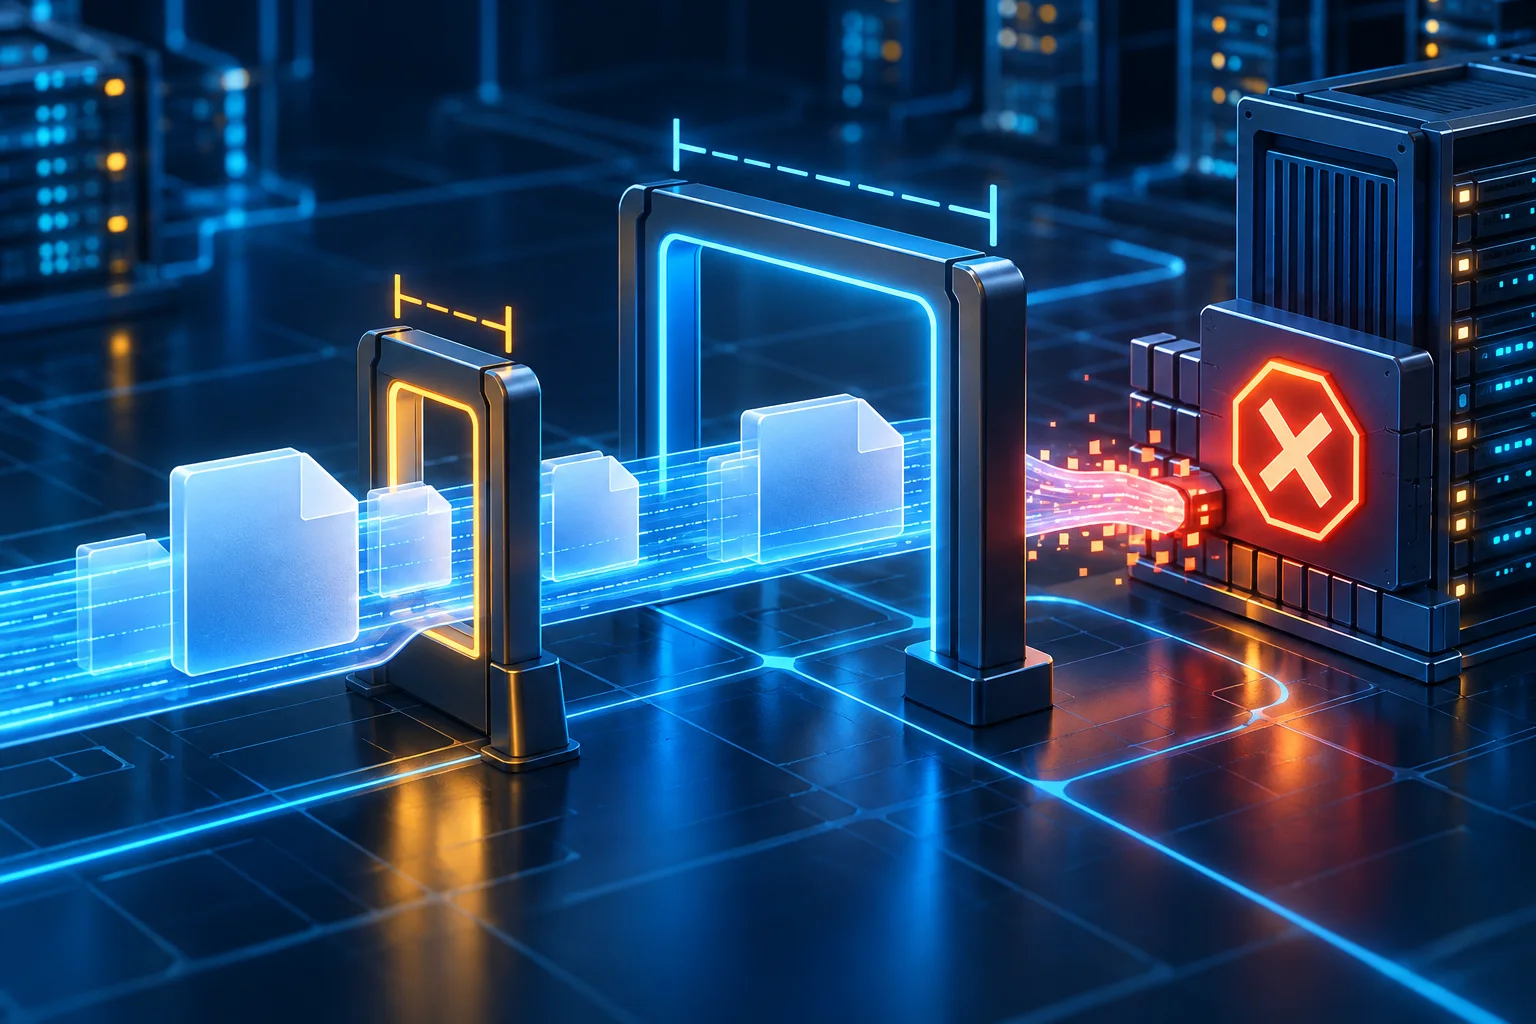
If a PHP upload form works with small files but returns an empty $_FILES for larger ones, separate two limits before changing application code. upload_max_filesize applies to one file. post_max_size applies to the entire POST body, including all files and form fields, so it needs to be larger than the per-file limit.
Read PHP's upload error code first
When the request reaches PHP, $_FILES['document']['error'] helps identify what happened. UPLOAD_ERR_INI_SIZE points to a PHP configuration limit, UPLOAD_ERR_FORM_SIZE to the form's own limit, and UPLOAD_ERR_PARTIAL to an incomplete transfer. Do not assume the temporary file exists or is safe to process when the error is not UPLOAD_ERR_OK.
$file = $_FILES['document'] ?? null;

if ($file === null || $file['error'] !== UPLOAD_ERR_OK) {
    // Log the error code and request ID;
    // show a limited, user-friendly message.
}
UPLOAD_ERR_NO_FILE means no file was selected; it is not a size-limit error. A missing field, a PHP upload error and a web-server 413 response are different observations. Correlate them with the access and error logs instead of folding every case into one generic message.
A 413 may happen before PHP runs
A web server, reverse proxy or CDN can reject a request body before it reaches PHP. In that case the application may never receive the expected fields, and the relevant log will show the response or request-body limit at that layer. Changing only php.ini will not change a limit enforced by the proxy or web server in front of PHP-FPM.
Check the effective configuration for the SAPI serving the request. Raising the limits also increases the memory and concurrency impact of large uploads; streaming, chunking or direct-to-object-storage uploads may be a better fit for large files. PHP's references for upload error codes, common upload pitfalls and core configuration directives cover the PHP side.
Passing a size check does not make a file safe. Do not trust a client-supplied MIME type; review authorization, generated filenames and storage location separately in PHP file upload and security measures.
Related Articles
Comments (0)
Leave a Comment
Sponsors
Apps